New Delhi: The recent controversy surrounding NVIDIA founder and CEO Jensen Huang and reports of a possible foreign intelligence operation targeting him have raised serious questions about corporate cybersecurity, insider threats and the protection of sensitive business information.
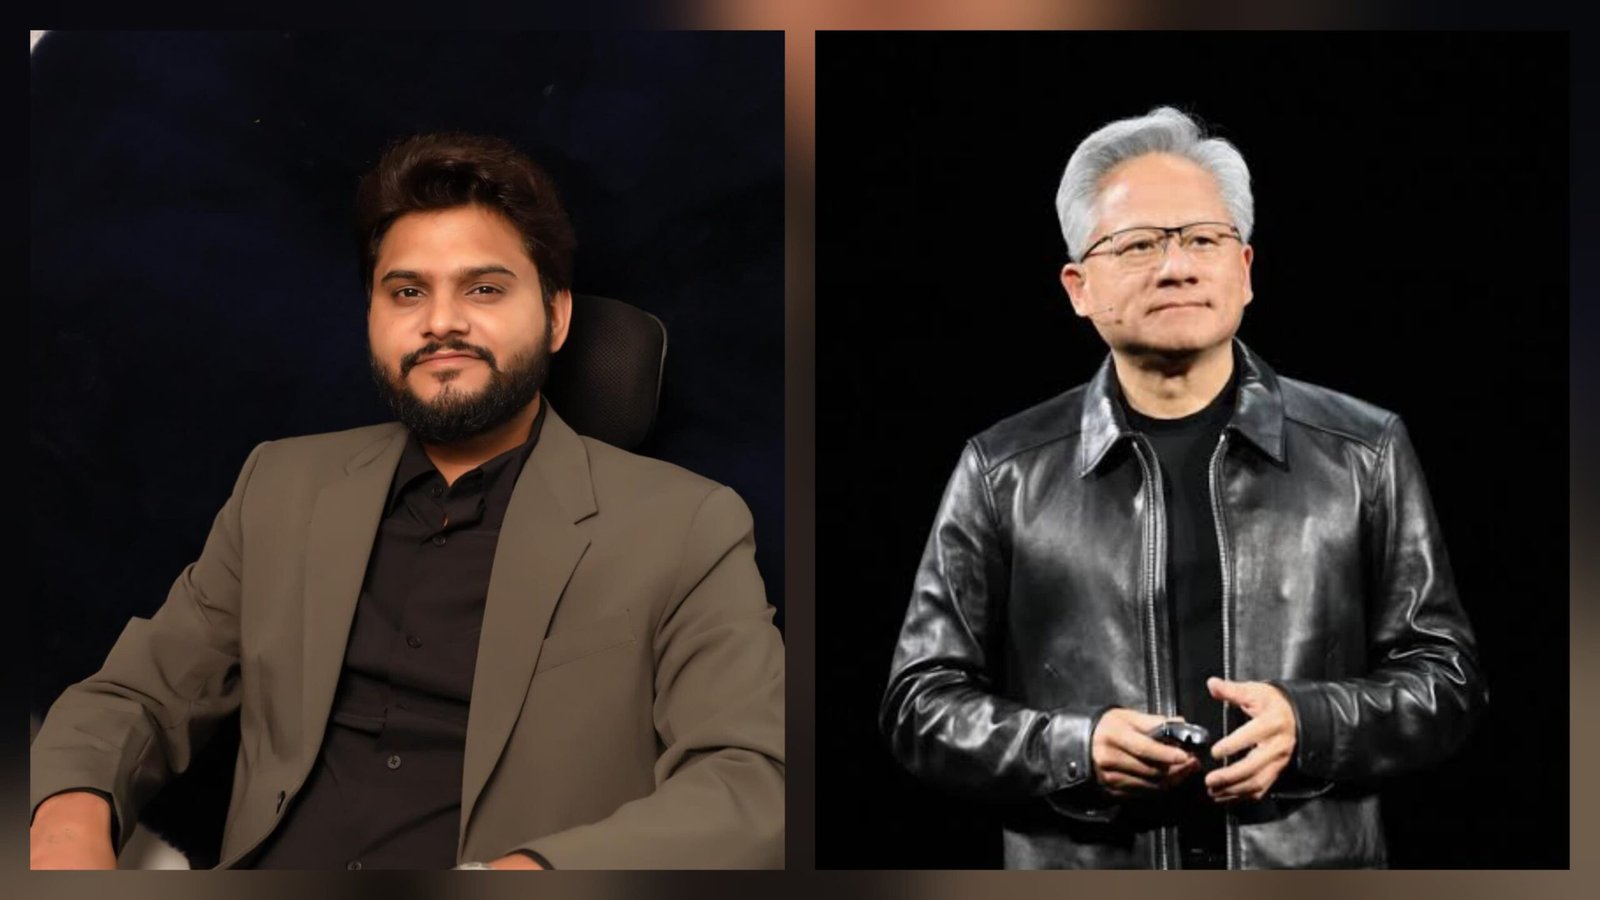
Addressing the broader security implications, Sunil Singh, Founder of VOLANSHQ and Founder of Securium Solutions, emphasises the urgent need for organisations to implement strict Zero Trust Security Policies to protect intellectual property, confidential information and critical business operations.
His message is clear: no individual, regardless of designation, reputation or authority, should receive unrestricted access to an organisation’s critical information.
Why the Jensen Huang and NVIDIA Developments Matter
The November 2026 developments involving Jensen Huang and NVIDIA have brought corporate security governance into the spotlight. Reports of a foreign intelligence effort targeting Huang prompted NVIDIA’s board to announce an independent investigation. The board stated that it had no reason to believe company secrets or national security had been compromised.
For cybersecurity professionals, the broader lesson goes beyond NVIDIA. Corporate espionage, insider threats, social engineering and unauthorised information sharing can expose even the world’s most influential technology companies to significant risks.
Sunil Singh’s Message: Never Trust, Always Verify
Sunil Singh believes organisations must move away from traditional security models that automatically trust employees, executives, vendors or business partners.
He advocates a strict Zero Trust Security Policy based on the principle of Never Trust, Always Verify.
Under this approach, every user, device, application and access request must undergo appropriate verification, regardless of designation or location.
Singh emphasises that cybersecurity policies must apply equally to founders, CEOs, board members, senior executives and external consultants.
Five Zero Trust Policies Every Organisation Should Implement
- Identity Verification: Implement Multi-Factor Authentication (MFA) and privileged identity management.
- Least Privilege Access: Provide employees access only to information necessary for their responsibilities.
- Continuous Monitoring: Monitor suspicious logins, unusual downloads and confidential data transfers.
- Insider Threat Management: Establish mechanisms to identify and investigate potential insider risks.
- Third-Party Security: Regularly assess vendors, consultants and external technology partners.
Who Is Sunil Singh?
Sunil Singh is the Founder of VOLANSHQ and Founder of Securium Solutions. He is a cybersecurity entrepreneur and business leader working across information security, enterprise compliance and technology management.
With an MBA and professional cybersecurity qualifications, including CISM, LPT and OSCC, he has experience across healthcare, finance and manufacturing.
Through Securium Solutions, he is associated with cybersecurity consulting, VAPT, information security audits, digital forensics and Governance, Risk and Compliance.
Through VOLANS HQ, he is focused on helping B2B SaaS startups become enterprise-ready through compliance and security capabilities, including SOC 2, ISO 27001, PCI DSS and SIEM.
Zero Trust Must Become a Corporate Governance Priority
The Jensen Huang and NVIDIA developments reinforce the importance of protecting sensitive information through structured security policies rather than relying solely on individual reputation or internal trust.
Sunil Singh believes Zero Trust should become a corporate governance priority, supported by leadership, compliance teams and independent security assessments.
His message to business leaders is simple: No individual is bigger than an organisation’s security policy. In modern cybersecurity, trust must be earned through continuous verification, not granted through designation.